All projects
PocketVault
LiveMobile / PWAOffline TOTP authenticator with encrypted storage, a PIN lock and optional biometric unlock.
Stack
- React
- Vite
- TypeScript
- Tailwind CSS
- Web Crypto API
- WebAuthn
- IndexedDB
- PWA
What to demo
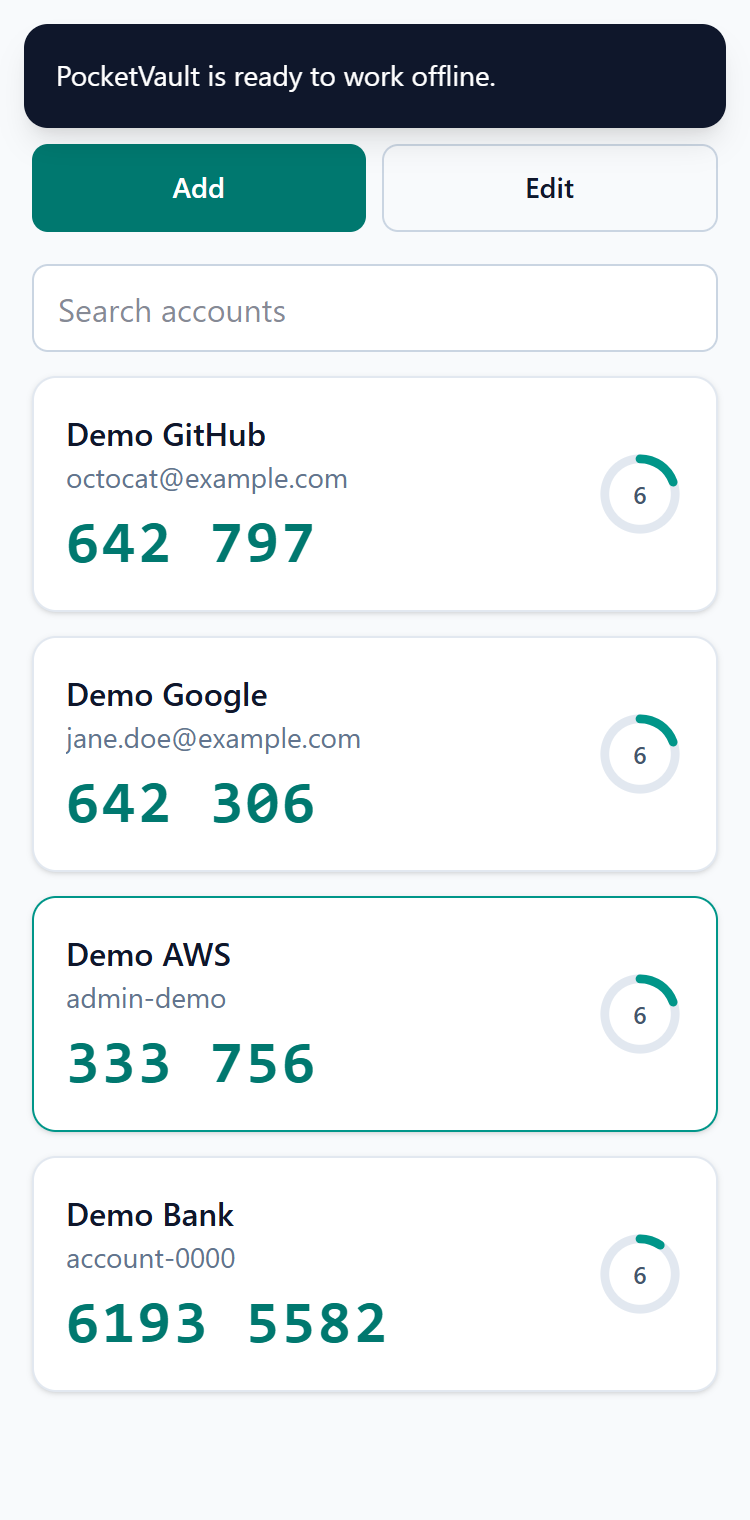
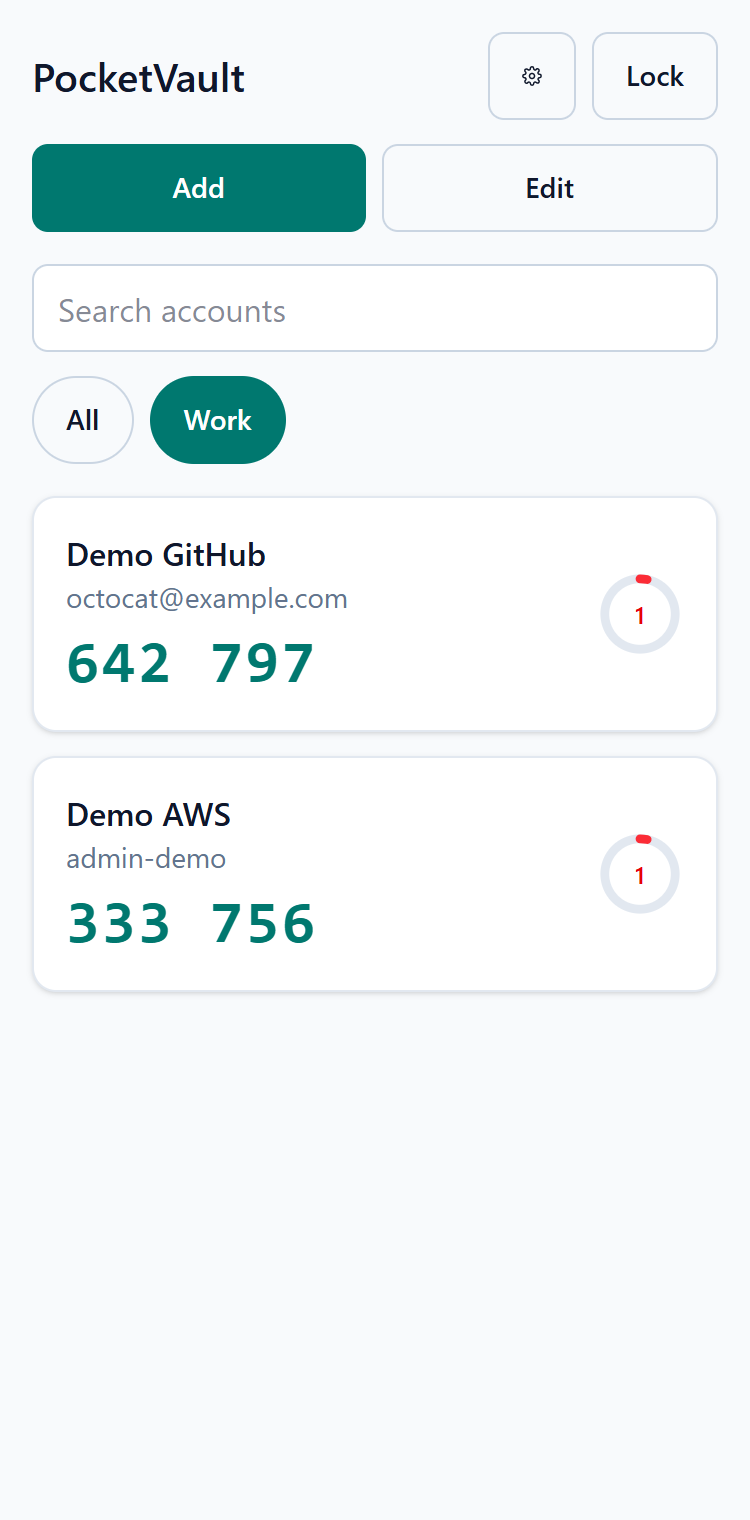
- Create a PIN and watch the demo accounts show live codes with a countdown ring
- Go offline, reload and unlock: everything still works
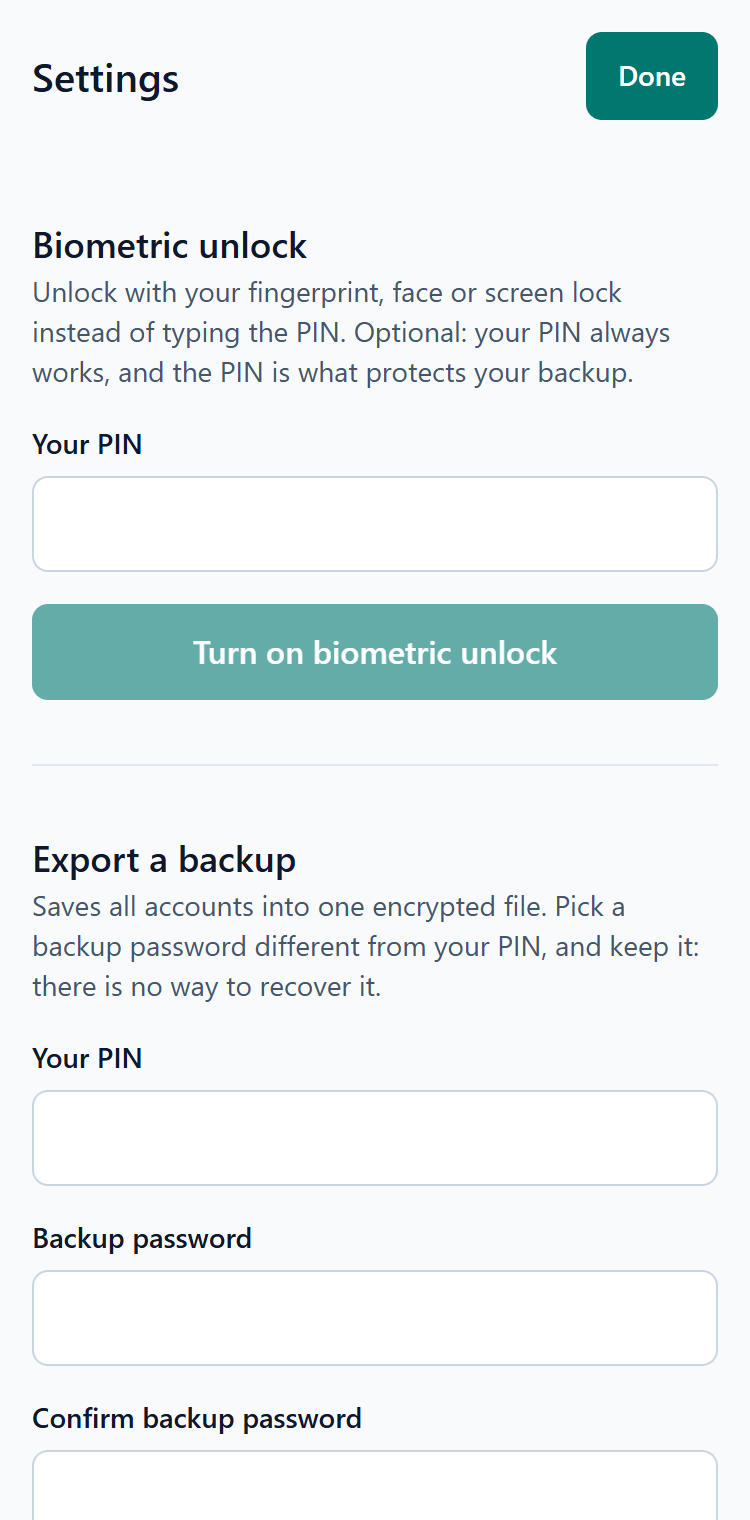
- Enter a wrong PIN three times to see the lockout, then export an encrypted backup
Architecture
- The TOTP and HOTP engines use Web Crypto HMAC (SHA-1, SHA-256, SHA-512) and are checked against the RFC 6238 and RFC 4226 test vectors.
- A PIN-derived key (PBKDF2) encrypts each secret with AES-GCM. The key lives in memory only and is cleared on lock, so IndexedDB never holds a plaintext secret.
- Wrong PINs trigger an escalating lockout that survives reloads, and the vault auto-locks when idle or backgrounded.
- Encrypted backups use a separate password; optional biometric unlock uses WebAuthn PRF where the device supports it.
- There is no backend: a service worker caches the app shell, so it installs as a PWA and makes no requests to other origins.